PE32 - Stack buffer overflow basic
Challenge Link:
https://www.root-me.org/en/Challenges/App-System/PE32-Stack-buffer-overflow-basicHere, First process of the pwn is always go to check the protection in the binary but the problem here is we cannot use checksec as we are previously using for the linux but don’t worry what we can do is we can either winchecksec or use ghidra or cutter I have used cutter in this challenge to check what are the protections in the binary.
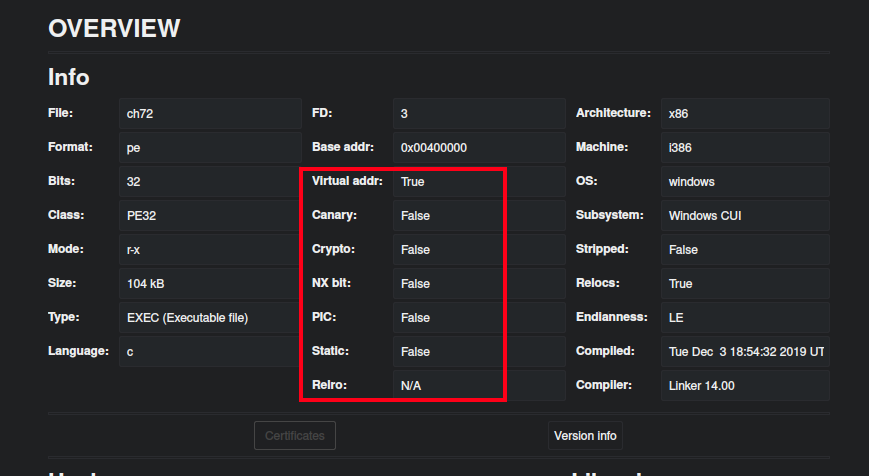
And you can see a lot’s of things are missing here like there is no canary no nx bit no relo either we can exploit this binary whatever we want to exploit if it will have bufferoverflow which makes us easy to exploit .