PE x86 - 0 protection
challenge
https://www.root-me.org/fr/Challenges/Cracking/PE-x86-0-protectionFirst step of reversing the binary is knowing how binary works let’s analyze the binary behaviour
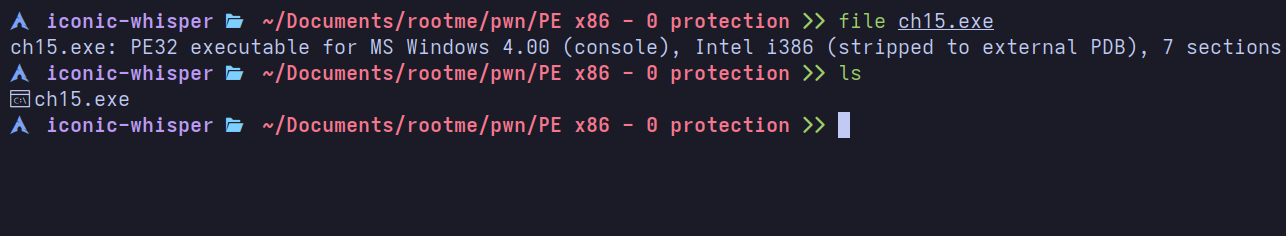
First thing we cann see is it’s the stripped binary which make very difficult to reverse it dynamically
so, I will go with the static reversing with ghidra
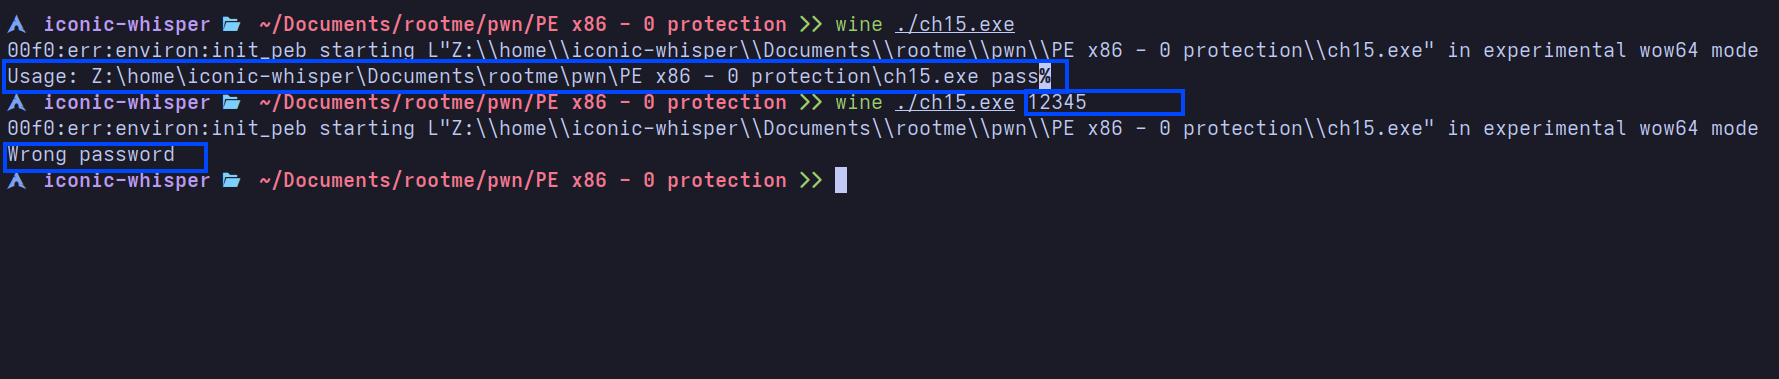
Here our first behavior of the binary is it asked for the password when it is executed as a parameter but also It makes one thing easy that it is printing the Wrong password this can be the advantage for me to get the password
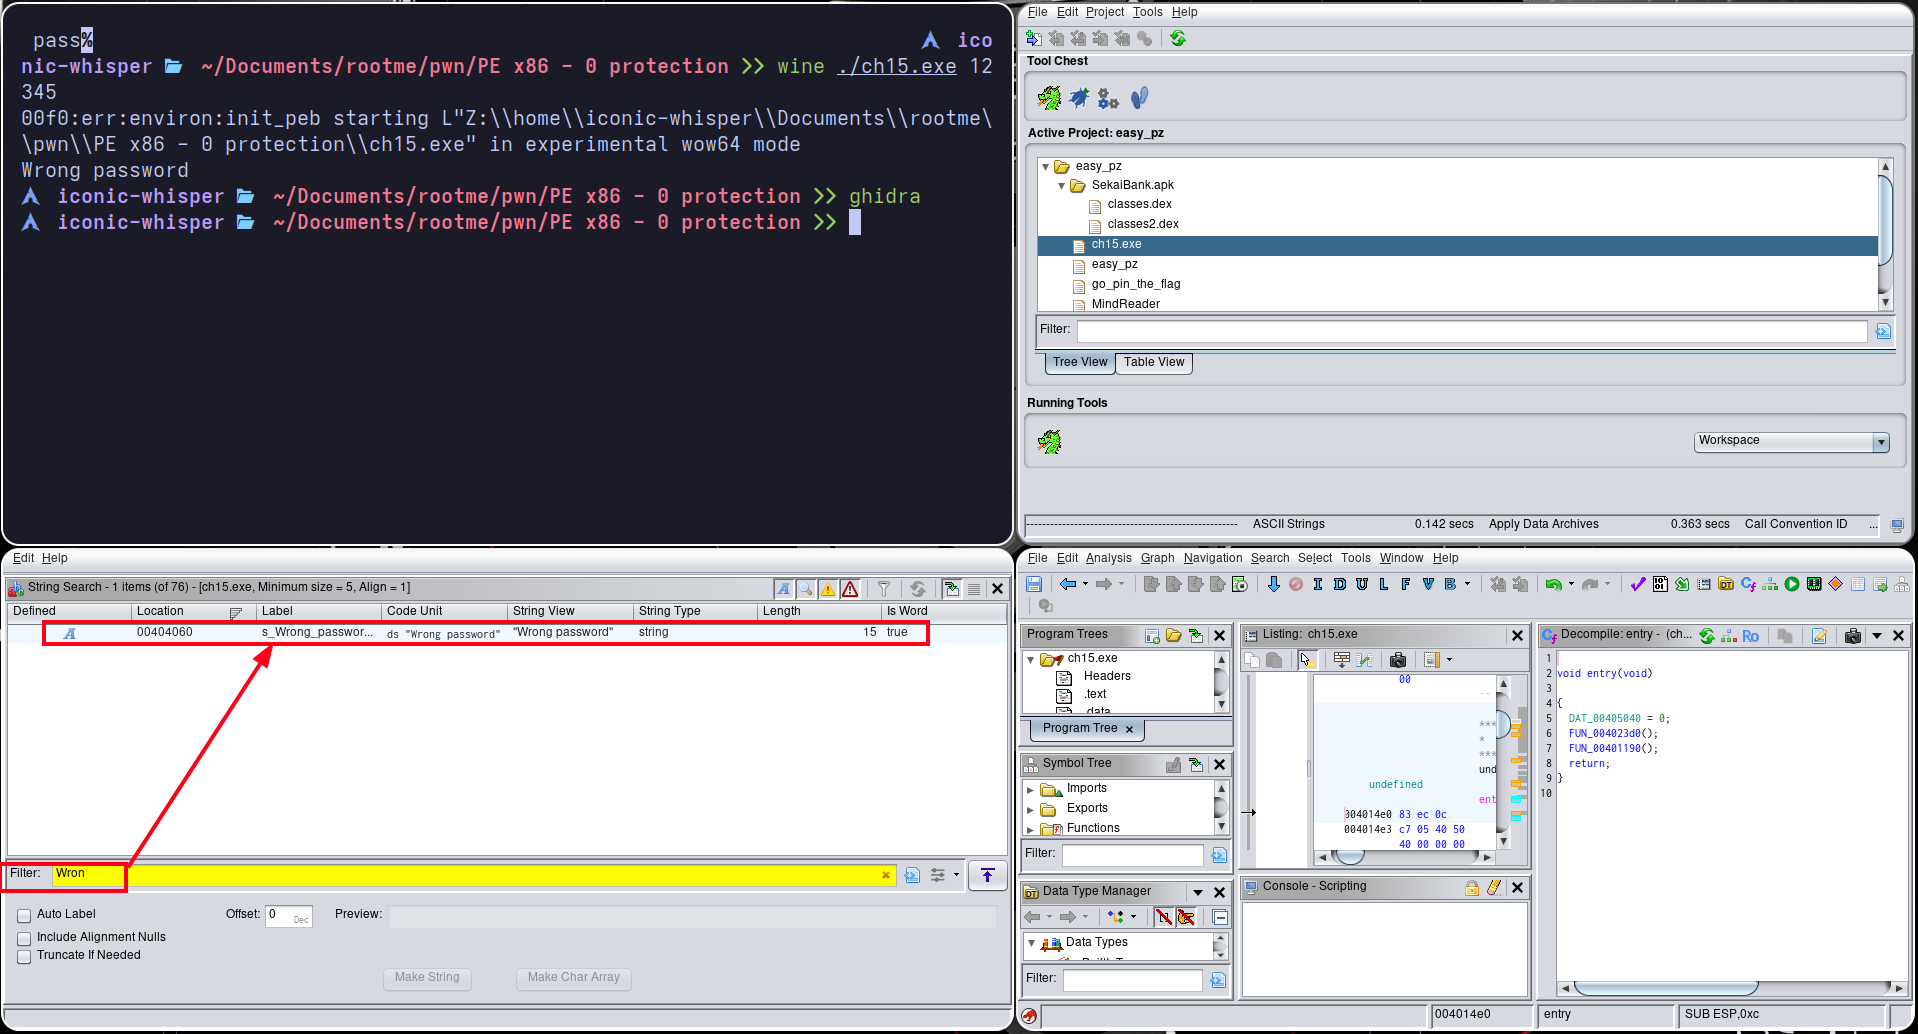
and we can visit the function which has compared this password and printed the result
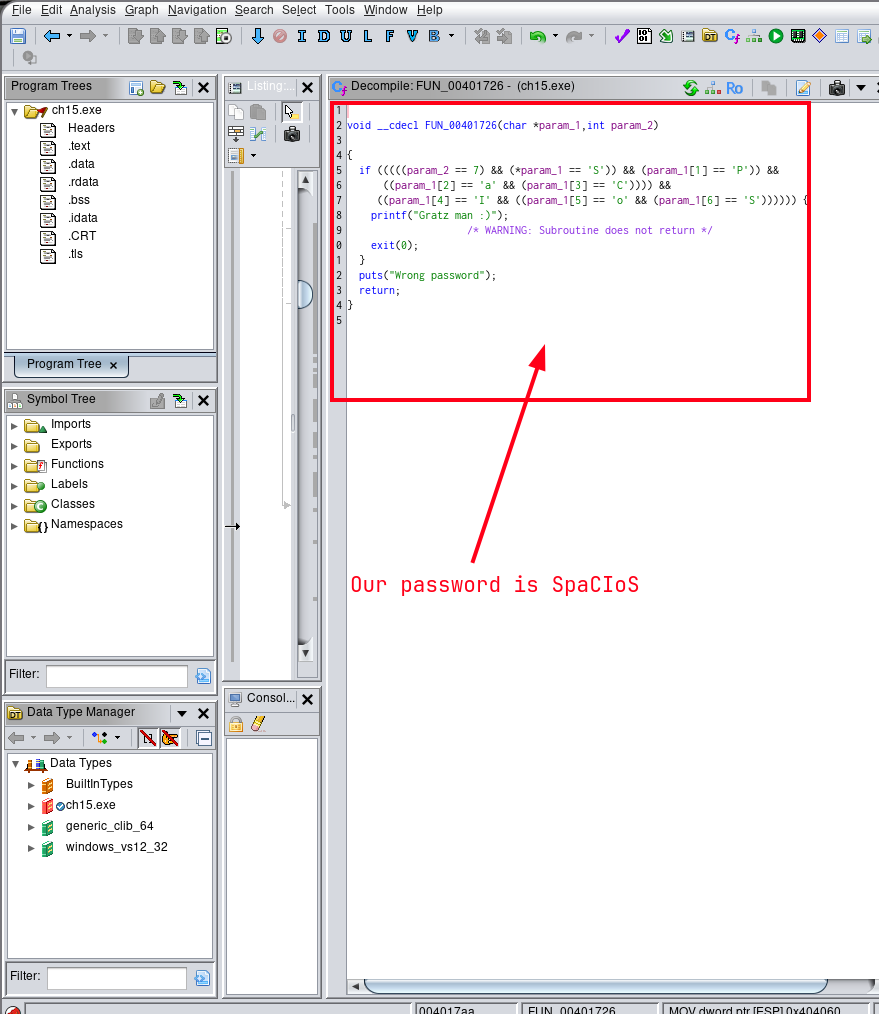
As one see Our password is SPaCIoS
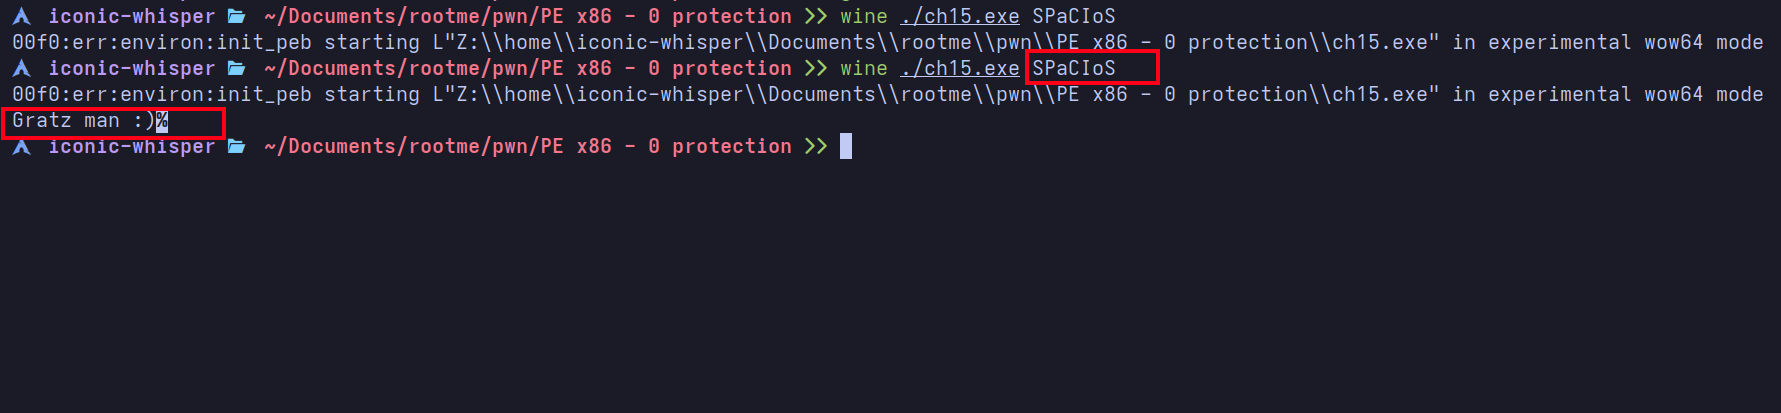
here we got the password